
Verdict: Malicious (phishing, high confidence). The GajShield honeypot captured this email on 21 September 2026. It poses as a cloud storage billing alert and claims a $2.99 charge for a 250 GB plan was declined.
The goal is to push the recipient into a staged "renewal" funnel. Our analysts followed the link in a controlled environment: after a fake countdown and two scare pop-ups, the victim lands on a discounted antivirus sales page. The pattern points to affiliate fraud, where scammers earn a commission for each sale they push, with possible card harvesting along the way. The campaign is sent from rented Google Cloud infrastructure. Its links point to Google Cloud Storage buckets, which lets them inherit Google's domain reputation and get past URL filters.
All original email addresses in this report are redacted: [recipient-redacted] for the honeypot mailbox and [sender-redacted] for the spoofed sender.
| Field | Value |
|---|---|
| Capture source | GajShield email honeypot |
| Received | 21 Sep 2026, 23:24:09 IST (17:54:06 UTC) |
| Subject | Payment Declined: Avoid Automated File Cleanup |
| Display name | Cloud Payment Alerts |
| Sender | [sender-redacted] at sproutnews.com |
| Recipient | [recipient-redacted] (honeypot mailbox) |
| Sending IP | 8.235.84.97 (Google Cloud, 97.84.235.8.bc.googleusercontent.com) |
| Message-ID domain | sproutnews.com (random 32-character hex local part) |
| Content type | Single-part text/html, UTF-8, no plain-text alternative |
| Lure | $2.99 "250 GB Plan" charge declined for September 2026 |
| Call to action | "Reactivate Today" button |
The headers show a message sent directly from a disposable cloud VM, not from any billing or storage provider's mail system.
Received: from sproutnews.com (97.84.235.8.bc.googleusercontent.com [8.235.84.97])
    by mail2.gajshield.com (8.14.7/8.14.7) with SMTP id 68LHs8GK014472
    for <[recipient-redacted]>; Mon, 21 Sep 2026 23:24:09 +0530
From: Cloud Payment Alerts <[sender-redacted]>
Subject: Payment Declined: Avoid Automated File Cleanup
Message-ID: <db9044aa9484450fa72a8658ad927b7a@sproutnews.com>
Date: Mon, 21 Sep 2026 17:54:06 +0000
Received line. The client said HELO sproutnews.com, but reverse DNS resolves to a Google Cloud compute instance (*.bc.googleusercontent.com). Real billing mail passes through the provider's own outbound relays.with SMTP rather than ESMTP/ESMTPS. That suggests a bare-bones bulk-mailing script, not a mature mail server.Date header (17:54:06 UTC) and the receive time (23:24:09 IST, or 17:54:09 UTC) are 3 seconds apart. The sender connected directly to our MX with no intermediate relays.The HTML is a polished, mobile-friendly "receipt card" built to look like a legitimate billing notice. It uses standard psychological pressure tactics.
Both links in the email point to Google Cloud Storage (GCS), a technique known as trusted-service abuse.
| Link text | Destination (defanged) | Role |
|---|---|---|
| Reactivate Today | hxxps://storage.googleapis[.]com/jjmicdgo/m |
Entry point into the scam funnel |
| Unsubscribe | hxxps://storage.googleapis[.]com/jjmicdgounsb/m |
Same kit; the bucket name adds an "unsb" suffix |
storage.googleapis.com is a high-reputation Google domain used by millions of legitimate sites. Many URL filters and email gateways allow it by default, so the attacker's real landing page never shows up in the email.jjmicdgo are random strings. Creating new ones costs almost nothing, so blocking a single bucket has little lasting effect.m. A file with no extension hides what the object does. It typically serves an HTML page or a JavaScript redirect that forwards the visitor to the next stage.We followed the "Reactivate Today" link in an isolated analysis environment on 22 September 2026. The funnel took about a minute to click through and ended on a discounted antivirus sales page, not a storage provider.

Each stage adds another layer of fear, reassurance, or urgency before the final sale.
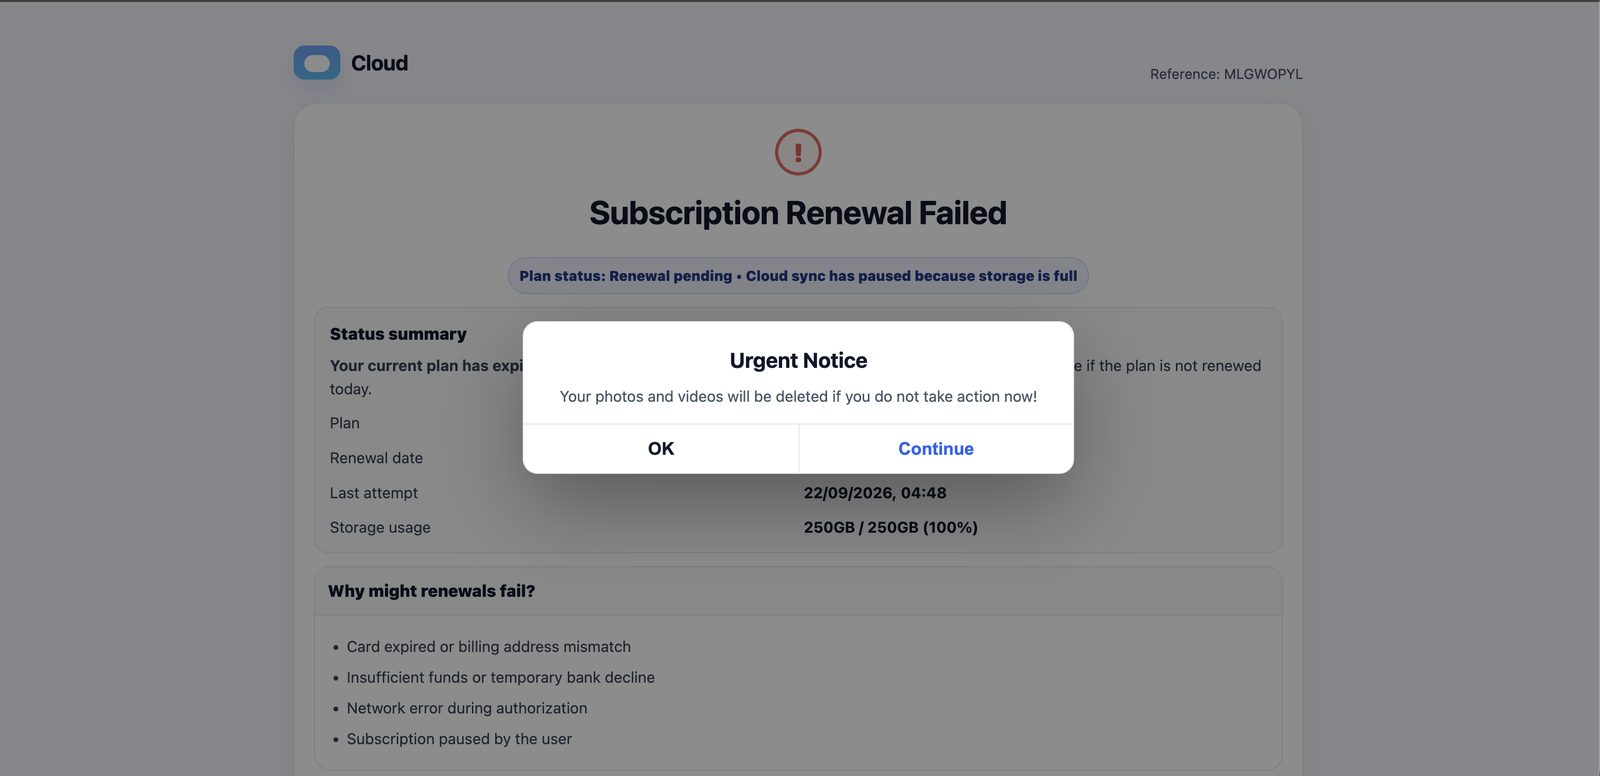
The page opens on a generic "Cloud" brand with a random reference code, MLGWOPYL. A pop-up styled like a native iOS or macOS system alert appears immediately: "Your photos and videos will be deleted if you do not take action now!" It offers both "OK" and "Continue", but either choice keeps the victim on the scam page.
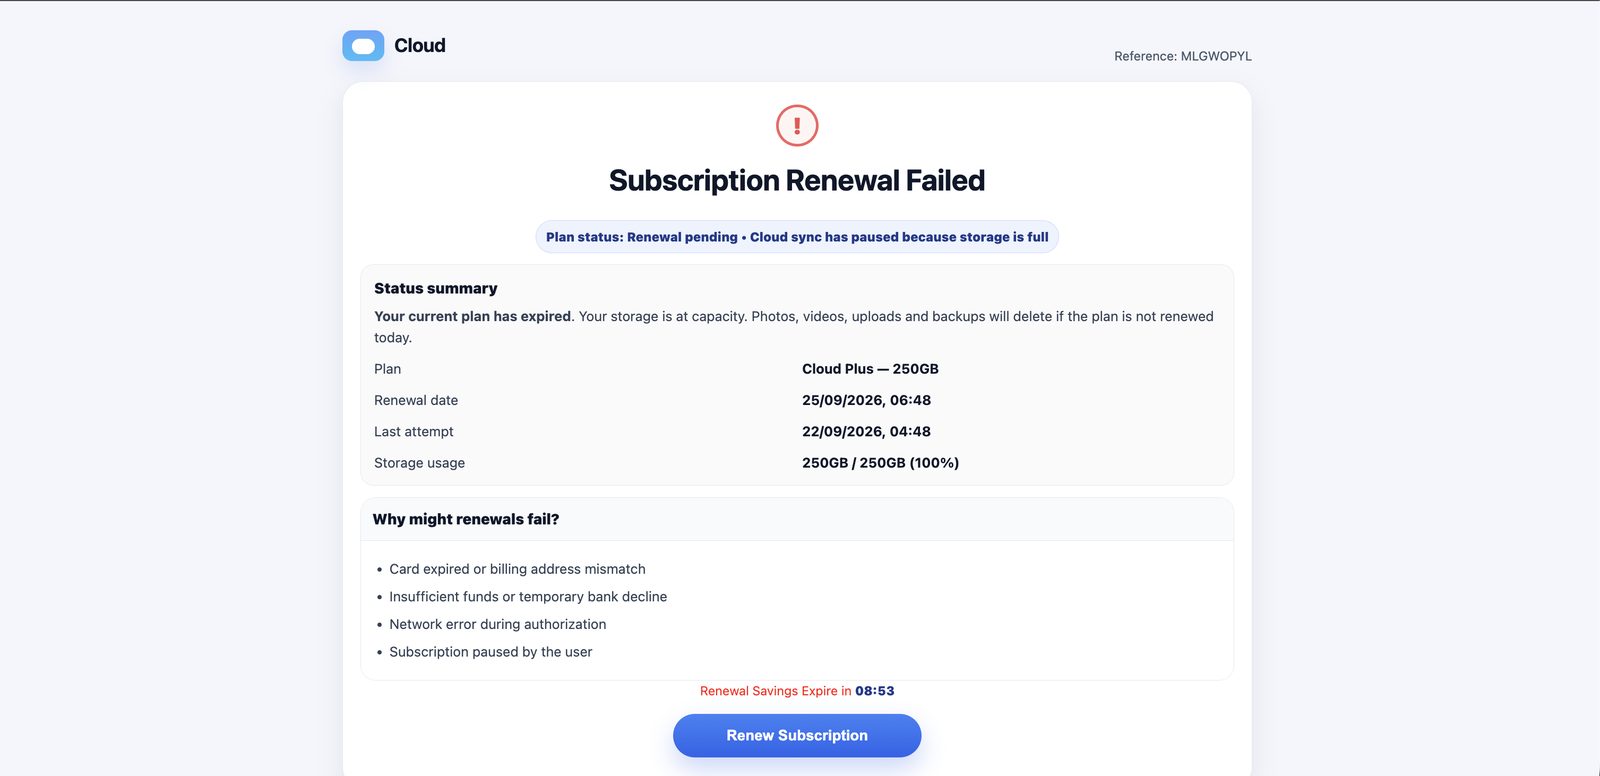
The page claims "Subscription Renewal Failed" for a "Cloud Plus — 250GB" plan with storage at 250 GB / 250 GB (100%). Several details give it away:
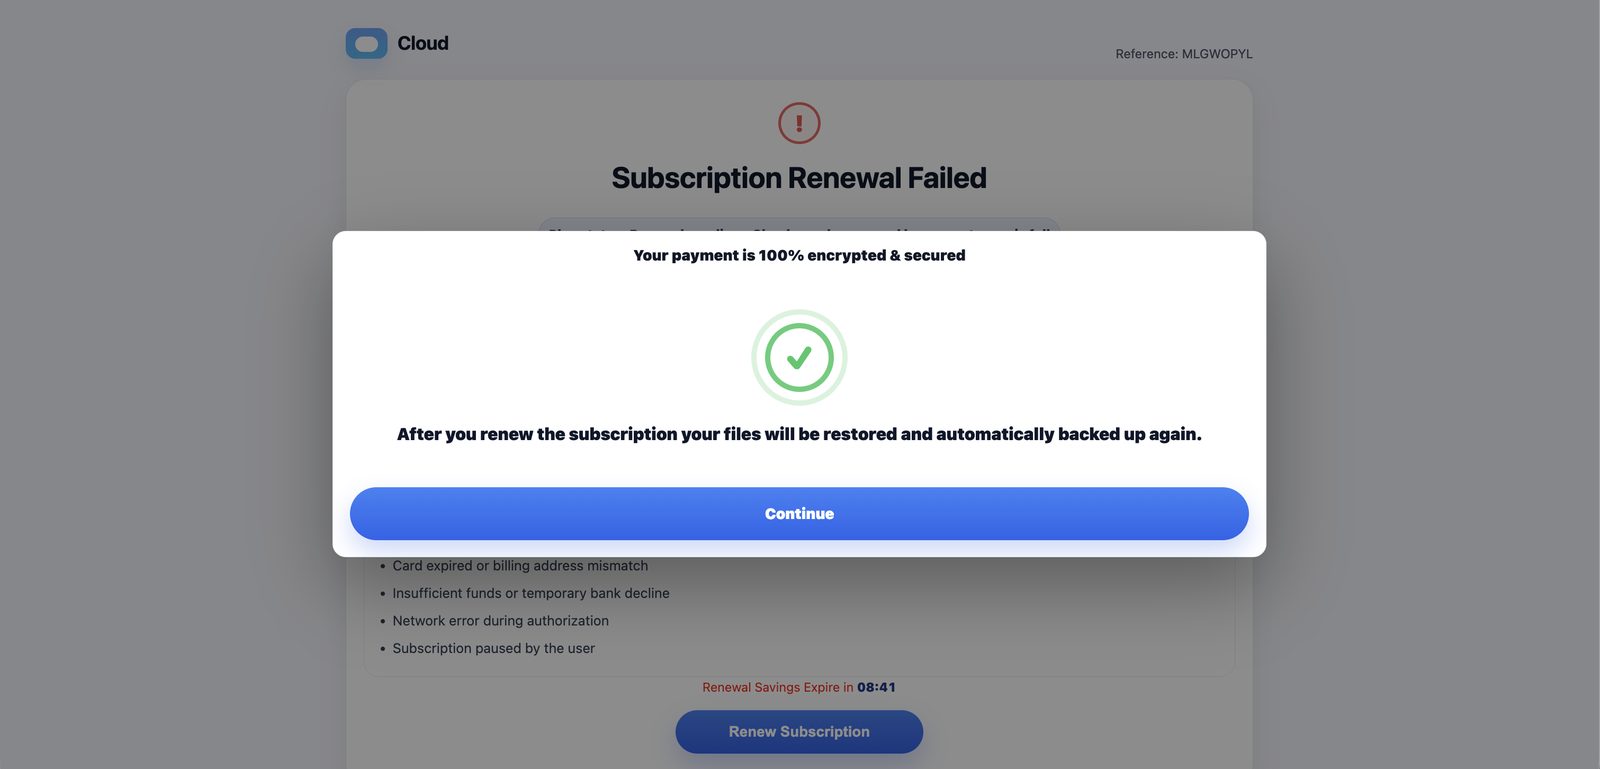
Clicking "Renew Subscription" opens a modal saying the payment is "100% encrypted & secured" and that files "will be restored and automatically backed up again". There is no payment form here. The pop-up exists only to calm the victim right before the hand-off.
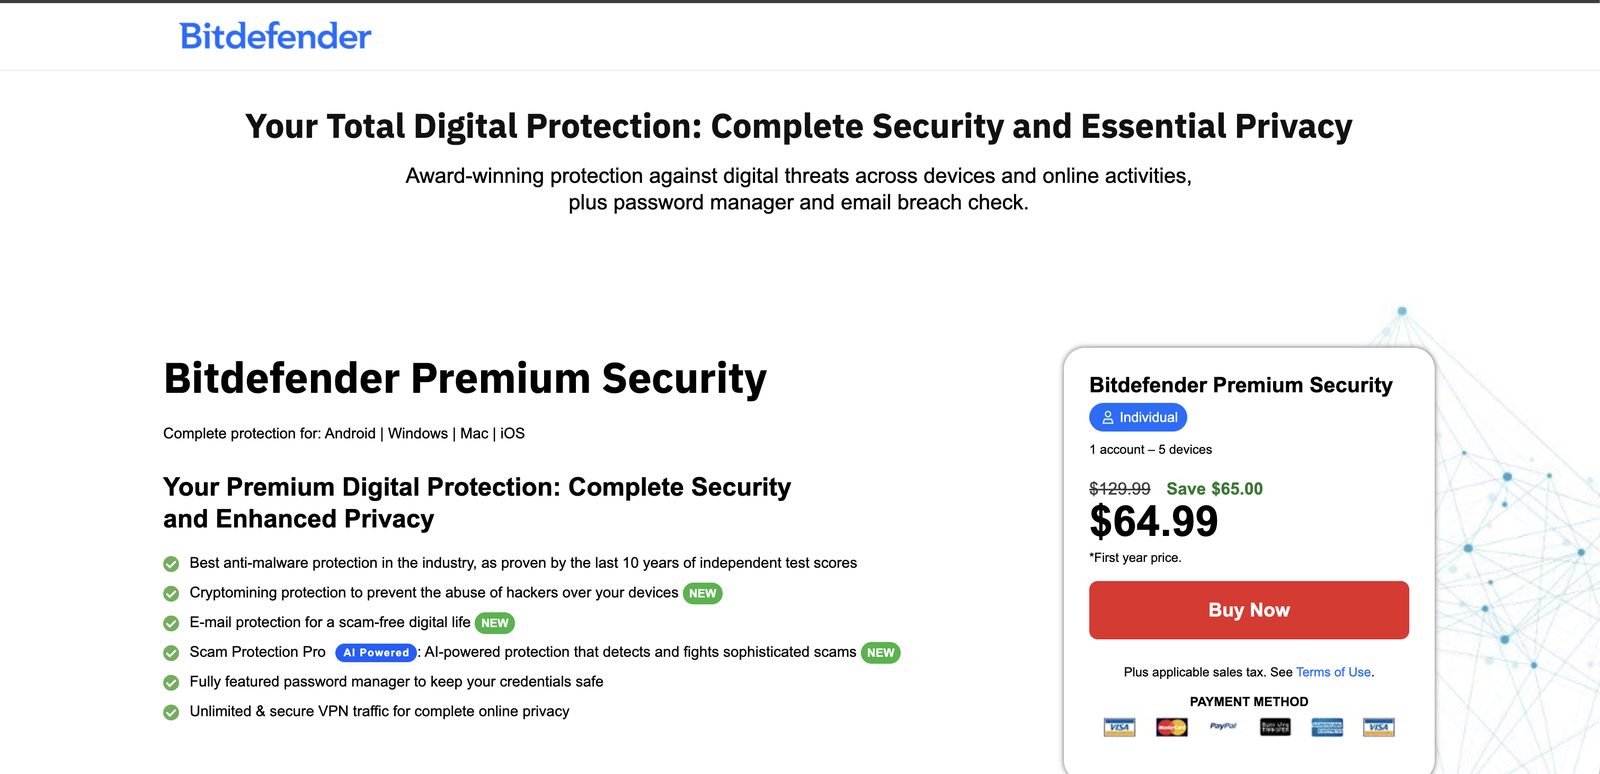
"Continue" leads to a Bitdefender Premium Security sales page priced at $64.99 for the first year, down from $129.99. The cloud storage story disappears completely.
This is a well-known monetisation model for storage-full scams. The operators join affiliate programs and earn a commission on every sale they drive, using fear instead of advertising. Bitdefender is not involved in the campaign; its brand is being abused. Scam traffic of this kind usually passes through a traffic distribution system that decides where to send each visitor. Another victim, or the same one on a different day, may land on a different product or on a card-harvesting form.
The screenshot does not show the final URL, so we cannot yet confirm whether this was the vendor's genuine store reached through an affiliate link or a cloned checkout page. The low-resolution payment icons, with the Visa logo shown twice, are worth a closer look. Either way, victims should not buy anything reached through this funnel.
All URLs are defanged. Bucket names and sending domains rotate quickly, so treat these as hunting leads rather than long-lived block entries.
| Type | Indicator | Notes |
|---|---|---|
| IPv4 | 8.235.84.97 |
Sending host, Google Cloud VM |
| rDNS | 97.84.235.8.bc.googleusercontent[.]com |
Google Cloud compute PTR |
| Domain | sproutnews[.]com |
HELO, From and Message-ID domain |
| URL | hxxps://storage.googleapis[.]com/jjmicdgo/m |
"Reactivate Today" entry point |
| URL | hxxps://storage.googleapis[.]com/jjmicdgounsb/m |
Fake "Unsubscribe" link |
| Subject | Payment Declined: Avoid Automated File Cleanup |
Exact subject line |
| Display name | Cloud Payment Alerts |
Sender display name |
| Body string | your account September be subject to automated file cleanup |
Kit find-and-replace artifact |
| Body string | Action Required: Payment Overdue For |
Banner text, month appended |
| Landing string | Renewal Savings Expire in |
Countdown label on the funnel page |
| Landing string | Your photos and videos will be deleted if you do not take action now! |
Fear pop-up text |
| Message-ID | <db9044aa9484450fa72a8658ad927b7a@sproutnews[.]com> |
Unique to this sample |
| Tactic | Technique | How it appears here |
|---|---|---|
| Resource Development | T1583.006 Acquire Infrastructure: Web Services | GCS buckets host the funnel entry points |
| Resource Development | T1583.003 Acquire Infrastructure: Virtual Private Server | Google Cloud VM sends the mail |
| Initial Access | T1566.002 Phishing: Spearphishing Link | Email links to the external scam funnel |
| Execution | T1204.001 User Execution: Malicious Link | Victim must click "Reactivate Today" |
| Defense Evasion | T1036 Masquerading | Generic cloud-billing branding and native-looking alert pop-ups |
| Defense Evasion | T1656 Impersonation | Poses as the victim's own storage provider's billing team |
No single control stops this campaign, because every piece of it sits on trusted infrastructure. Layer your defences.
storage.googleapis.com, *.blob.core.windows.net, *.s3.amazonaws.com or similar object-storage hosts. Legitimate billing mail almost never links to a raw storage bucket.*.bc.googleusercontent.com, *.compute.amazonaws.com) rather than a known mail provider.This sample was captured by the GajShield email honeypot, which collects live threats to improve detections across GajShield products. All recipient and sender email addresses have been redacted.