
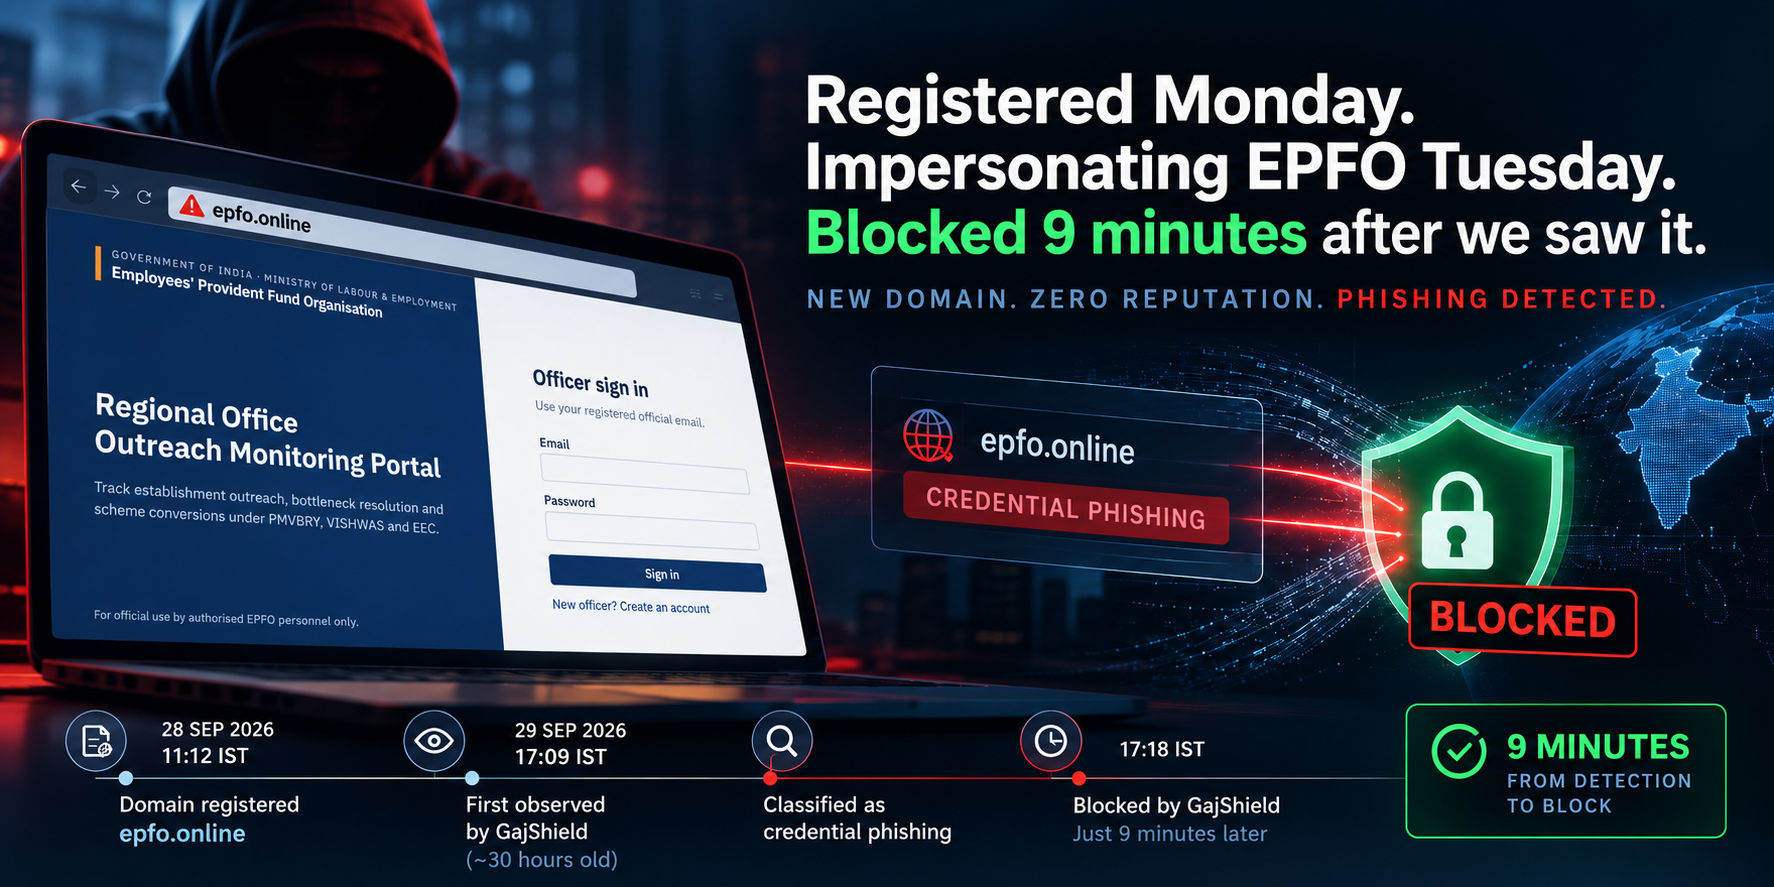
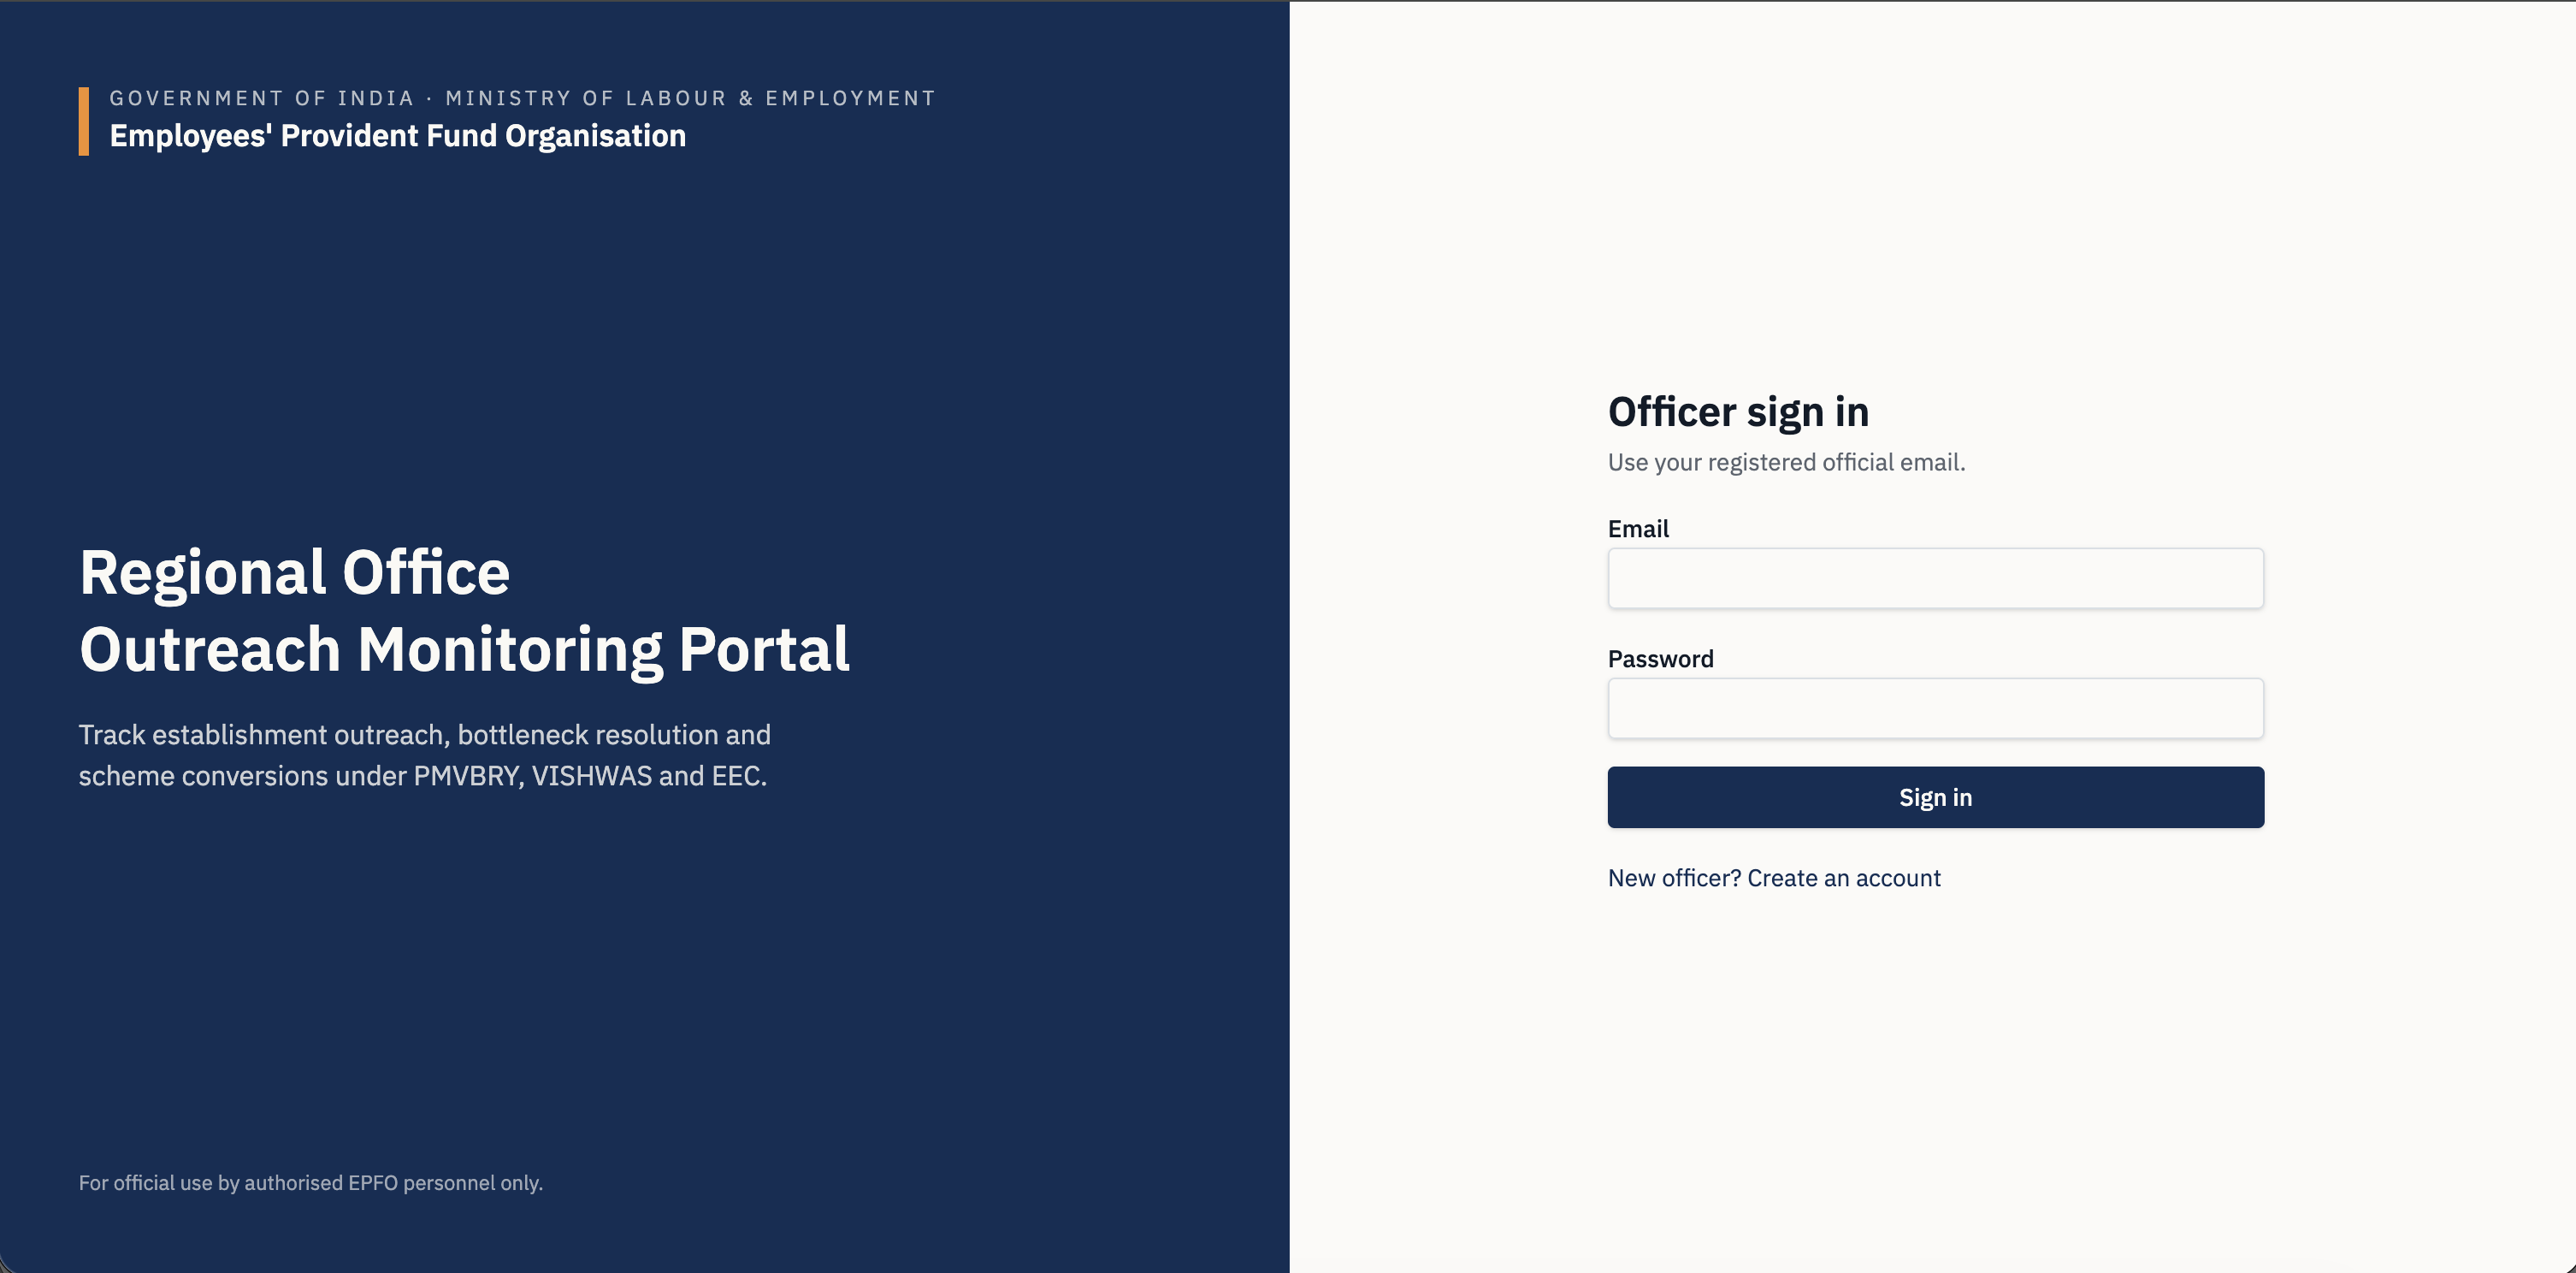
On 29 September 2026, a domain called epfo[.]online started serving a page titled "Sign in — EPFO Regional Office Portal," complete with a password field.
It had nothing to do with EPFO. The real portal is at epfindia.gov.in.
The timeline
→ Mon 28 Sep, 11:12 IST: domain registered, with the owner's identity hidden behind a privacy service
→ Tue 29 Sep, 17:09 IST: GajShield's engine first observed it
→ Tue 29 Sep, 17:18 IST: verdict issued. Credential phishing, blocked.
When we blocked it, the domain was about 30 hours old and still inside the registry's grace period for brand-new registrations. No blocklist had heard of it, so there was no reputation to go on. The verdict came 9 minutes after we first saw it.
Categorisation tells you what a site claims to be. Security has to tell you what the site actually is. A phishing page is designed to look exactly like the thing it impersonates, so any engine that classifies a site by what it appears to be about will get this wrong in the attacker's favour.
How we caught it (at a high level)
We don't wait for a domain to build a bad reputation. The engine evaluates new domains as soon as they appear and judges the live page on its intent, not only on its topic. A page that impersonates a government brand and asks for a password is phishing on day one. It isn't a financial services site.
Why this matters in India
EPFO accounts belong to crores of salaried employees. With a UAN and password, an attacker gets access to personal, employment and KYC details, which is enough to fuel further fraud. Setting up an attack like this now takes one cheap domain, an AI website builder and a free, automatically issued padlock. It can go from registration to live phishing in a day.
For employees
→ Use only epfindia.gov.in or the official UMANG app
→ Treat any EPFO link that arrives by SMS, WhatsApp or email as suspicious, whatever the padlock shows
→ If you entered your details on a lookalike site, change your password immediately and report it at cybercrime.gov.in or 1930
For security leaders
→ Ask your vendor how it handles domains that are hours old, not weeks old
→ Ask whether it judges a page by its intent or only by its category
→ An "allowed" category is not the same as a "safe" site
#CyberSecurity #Phishing #EPFO #ThreatIntelligence #India #NetworkSecurity #GajShield
Was this article helpful?
Your feedback helps us improve the knowledge base.